Skip to content
MenuClose

Security Intelligence

Understanding threats and the consequences of protective action.

We develop security intelligence for decisions that carry real consequences.

Security intelligence uses evidence and reasoning to understand threats, assess consequences, and choose protective action. Its scope includes software, identity, networks, AI agents, and the physical systems they influence. A security decision must account for the service being protected, the people who rely on it, and the disruption an intervention could cause.

We develop technologies and build companies that bring these questions into practice. Working from first principles means examining how a system functions, which assumptions its defenses rely on, and what evidence could expose a failure. Our work connects investigation, software assurance, preemptive defense, and controlled action. The problem determines which methods and expertise are needed.

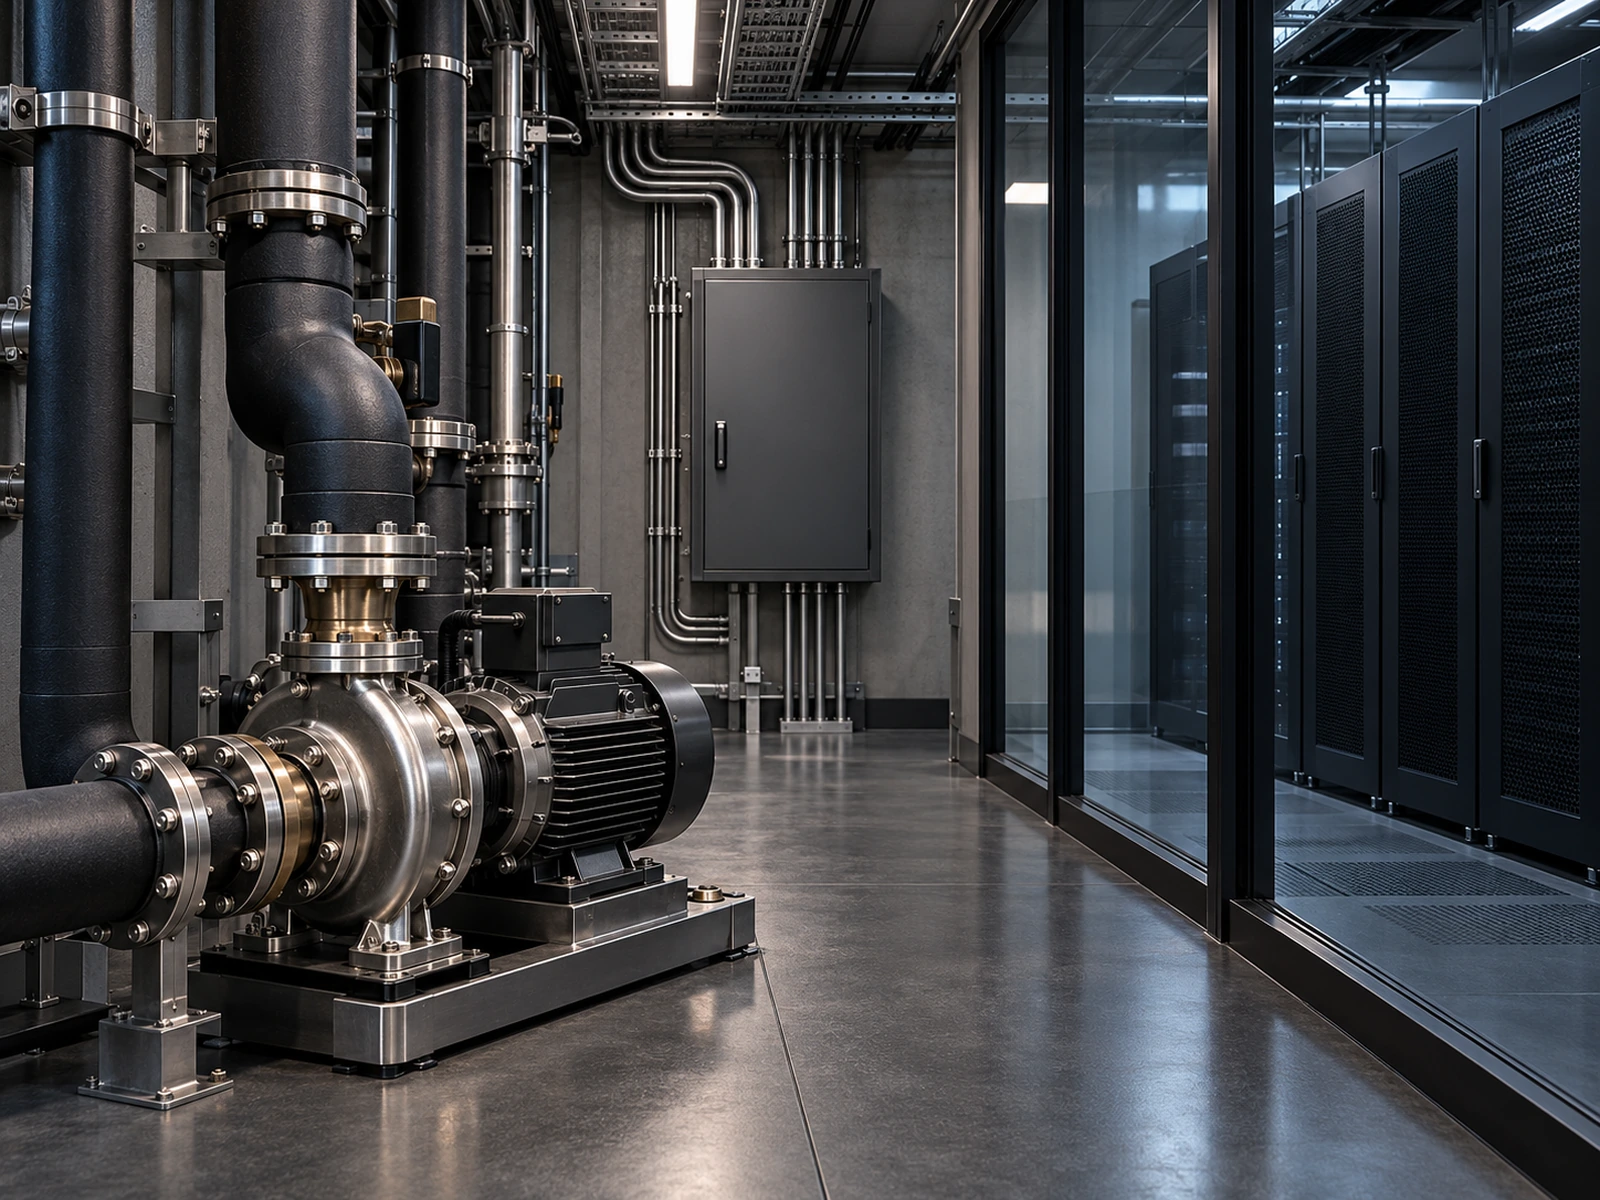
A precision test fixture on a dark surface: a steel shaft held in bearing blocks carries an encoder disc and a toothed wheel, each read by a cabled sensor.

Evidence and reasoning

An unexpected event can have several explanations: malicious activity, a component fault, or an ordinary change in operation. Useful security intelligence connects observations, examines their sources, and asks what would distinguish one explanation from another. Logs, identity records, and physical measurements can each reveal part of the picture. The strength of a conclusion should remain traceable to the evidence that supports it.
Conceptual illustration on black: translucent blue panels joined by fine lines of light, with a tall gold boundary between them. One path passes through a ring at the boundary's centre; another ends at a small gold mark on its edge.

Agentic security and controlled access

AI agents can examine software, gather evidence, and carry an investigation across tools and systems. Their access introduces questions of authority, delegation, and trust. Retrieved material may contain instructions intended to redirect an agent. We are interested in systems that keep evidence separate from authorization, constrain each action to an explicit scope, and verify what happened after execution.

Protective action begins with understanding what it will change.

Preemptive cybersecurity

Preemptive security begins by examining the conditions that allow harm: unnecessary access, exposed services, vulnerable software, and dependencies that can carry a failure into another system. It asks which changes would remove a credible route to harm while preserving legitimate work. Decisions should account for uncertainty, operational constraints, and the consequences of being wrong.

A maintenance session that remains open after its authorized window offers a concrete example. Closing that session requires current evidence, valid authority, and confirmation that the intended access ended. Those checks should also preserve the operator's legitimate session and the local controller's operation.

A remote session remains active after its maintenance window. An independently enforced policy limits the protective action to revoking that session, followed by checks of the connection states.

Read the full analysis

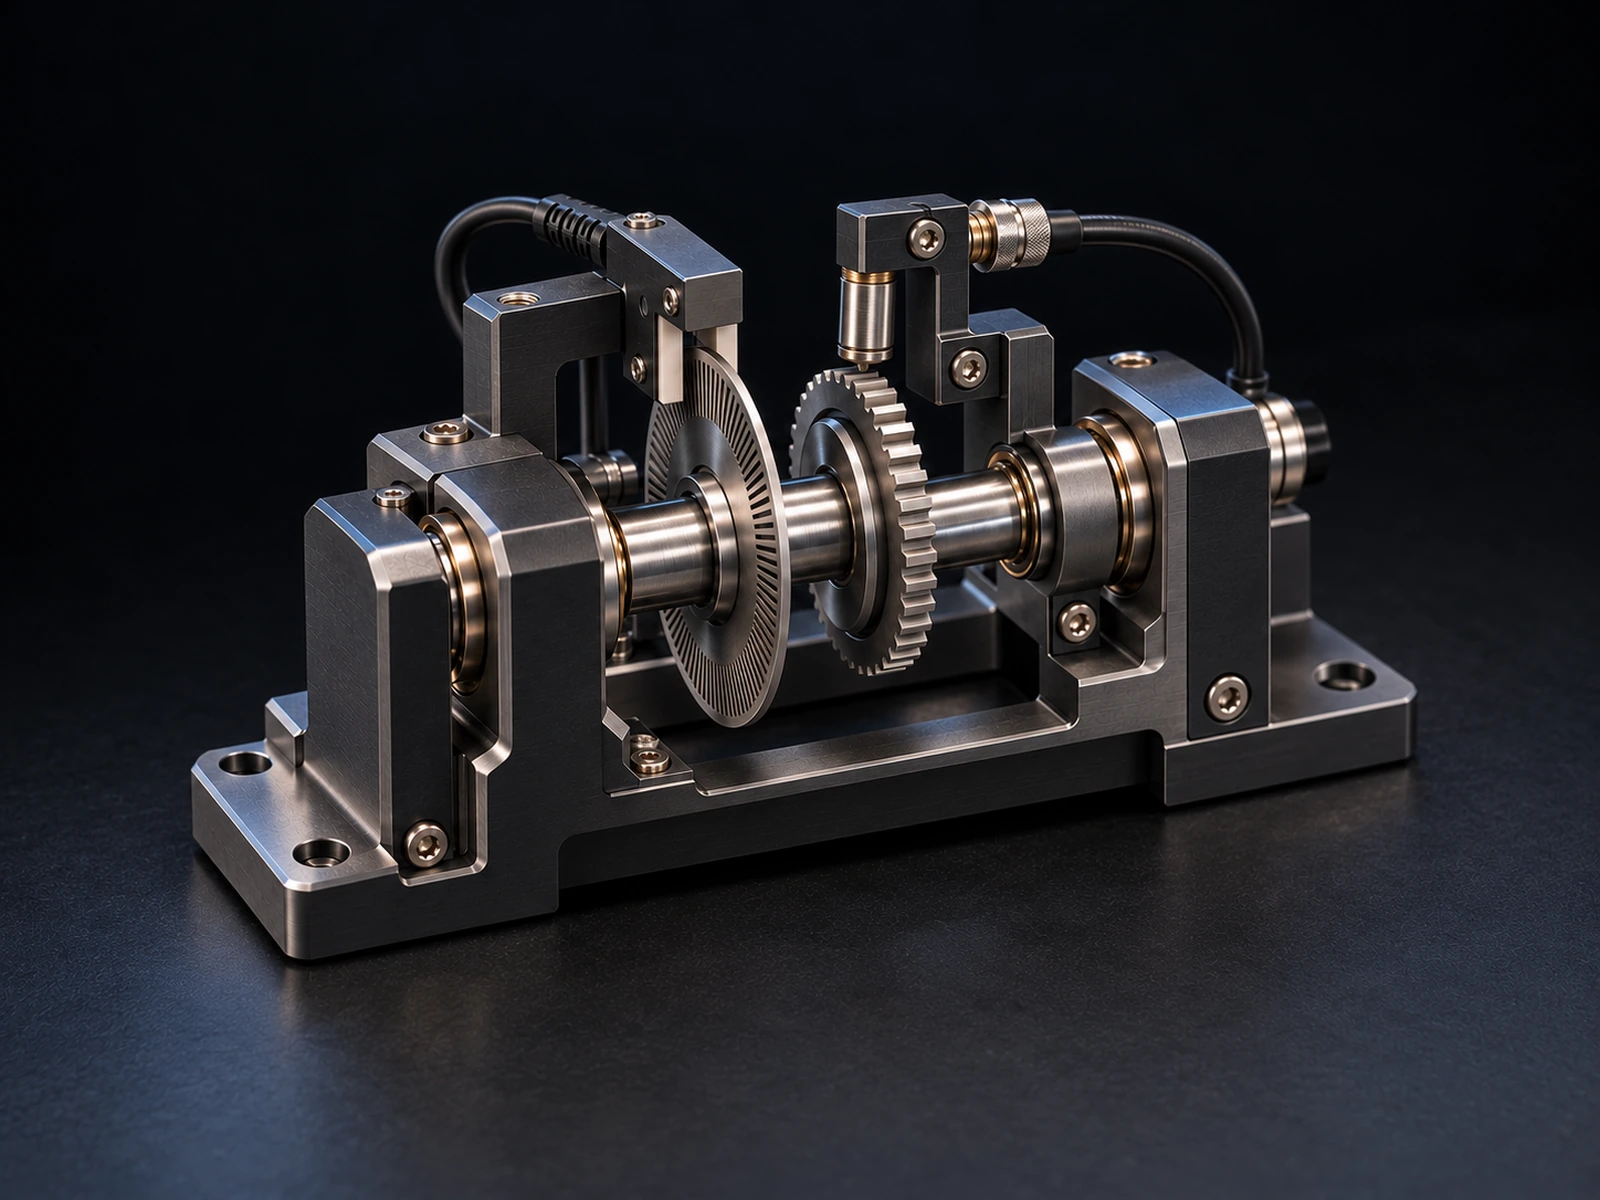
A plant corridor: an insulated pipe circuit and a stainless centrifugal pump in the foreground, a grey control cabinet fed by conduit on the back wall, and computing racks behind a glass partition at right.

Connected systems and physical consequences

Digital decisions reach into power, cooling, production, transport, and clinical operations. Extended operational technology (Extended OT) provides a useful way to examine the dependencies around these systems, including cloud services, remote access, and shared identities. The underlying questions remain concrete: what can influence the process, which protections operate locally, and how does the system behave when a dependency fails?

A dependency map becomes useful when it changes a decision. Security intelligence should help determine where intervention is warranted, what must keep running, and how recovery can be verified.

How we judge progress

A protective decision should withstand scrutiny before and after it is carried out.

Evidence that supports the conclusion
Can a reviewer trace the reasoning, examine competing explanations, and identify what remains uncertain?
Authority that can be enforced
Are scope, permissions, and expiry checked independently of the agent proposing the action?
Resilience under adversarial conditions
How does the system behave when inputs are manipulated, evidence is incomplete, or a required service fails?
Operational outcomes
Does protection reduce exposure while preserving legitimate work, limiting unnecessary intervention, and supporting recovery?

From the Journal

View Journal